Ortecha helped a US-based global bank manage and track compliance to a new enterprise data policy by mapping it to DCAM® capabilities and embedding it into a structured knowledge model. This created clear compliance roadmaps across business units, introduced evidence-based measurement and enabled audit-ready visibility aligned to BCBS 239 requirements.
The bank had taken a major step forward. A new enterprise data policy had been defined, with a clear two-year, thee step compliance schedule. But putting policy into practice across a global organisation is a different challenge.
The CDO Data Governance team needed a formal mechanism to interpret the policy, align it to data management capabilities and demonstrate progress over time across the Enterprise. This included the Business Unit operating levels that would support internal and external audit review with a focus on BCBS 239 compliance. There was no consistent way to do that.
At the leadership level, the question was simple. Are we compliant?
At enterprise scale, the answer was not.
This was not a documentation issue. It was a policy management problem.
The bank needed to:
This became even more critical with regulatory expectations such as BCBS 239 in scope.
Without a structured way to manage compliance, policy risk remained hidden, progress could not be measured and audit conversations relied on interpretation rather than evidence.
The bank needed more than a data capability assessment. It needed a way to connect its data policy to the capabilities required to comply with it, while also giving BUs a consistent way to measure and evidence progress.
That required experise across several layers at once: the bank’s policy and standards, DCAM, BCBS 239 and the technology needed to model the relationships between them.
As a premier EDM Council DCAM Partner, with deep roots in financial services and Solidatus platform expertise, we were chosen as the right fit to connect the pieces together.
We approached the challenge with structure, clarity and rigour.
We introduced a structured approach to policy compliance and management.
First, the bank’s data policy was mapped directly to DCAM capabilities. This created a clear link between what the policy required and what the organisation needed to do to meet it.
Next, a pilot assessment was run across the Americas business unit to establish a baseline view of capability maturity. This provided the first consistent measure of where the bank stood.
To prepare for the full global assessment of 10 business unites and approximately 80-sub units, we used Solidatus to create a multi-layered knowledge model that connected:
This model became the backbone of policy management, that did not just describe compliance – it showed it.
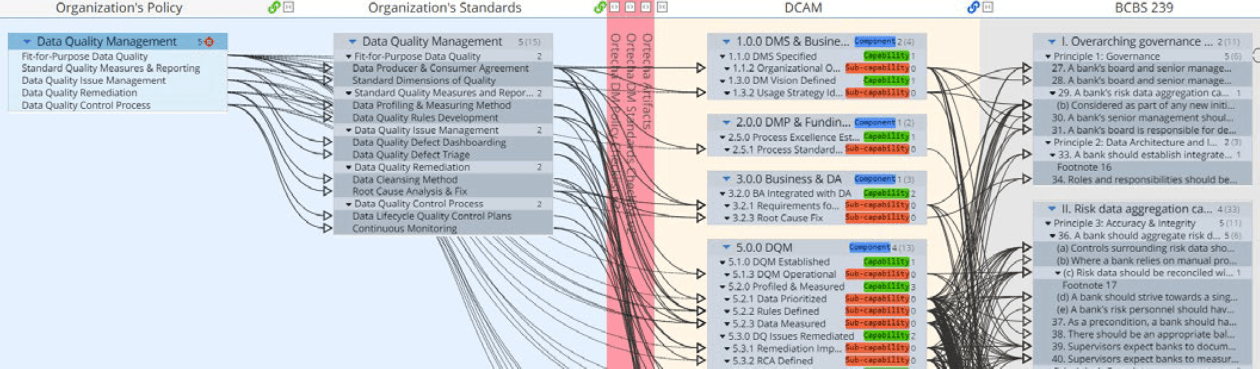
Policy compliance moved from static documents to a living, visual model of reality.
The Solidatus Knowledge Model made it possible to:
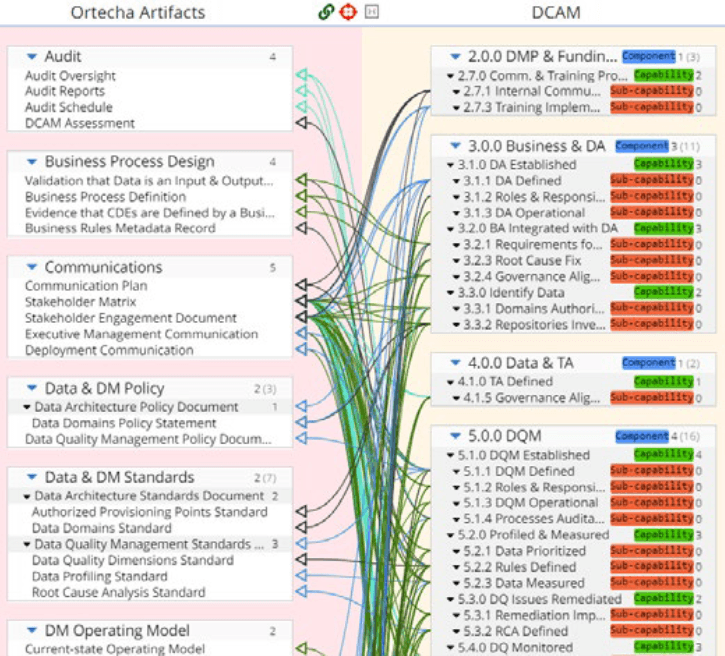
To strengthen this further, we introduced evidence-based scoring. Business units provided artefacts to support their capability scores. We then conducted a structured challenge review to ensure the evidence matched the assessment.
The result for the client? A consistent, defensible view of compliance across the enterprise.
The bank moved from fragmented policy interpretation to structured policy management.
Each business unit now had a clear compliance roadmap, aligned to both policy and regulatory expectations.
Most importantly, policy was no longer something to interpret – it became something the organisation could manage.
Policy compliance at this scale cannot be managed through documents and spreadsheets alone. The challenge is connecting what the policy says to what teams actually need to do, then measuring whether it is happening.
This engagement shows what becomes possible when you combine the right process, a globally recognised framework and the right platform.
DCAM provided a consistent way to define and assess the data management capabilities required. Solidatus made the relationships between policy, standards, BCBS 239 and those capabilities visible. We brought the methodology and practitioner expertise to connect the pieces, assess them consistently and challenge the evidence behind the results.
Together, that turned a complex policy compliance requirement into something the bank could actually manage: gaps could be seen, progress could be measured and compliance could be supported by evidence when challenged by internal or external audit
This is what good data management looks like: use proven standards, the right technology and a rigorous process to solve a real business problem.
A US-based Global Systemically Important Bank (G-SIB), operating across multiple regions and business units in a highly regulated environment. The organisation manages complex data landscapes and faces significant regulatory scrutiny, including BCBS 239 compliance requirements.

Founding Partner, Ortecha
| Cookie | Duration | Description |
|---|---|---|
| cookielawinfo-checkbox-analytics | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics". |
| cookielawinfo-checkbox-functional | 11 months | The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional". |
| cookielawinfo-checkbox-necessary | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary". |
| cookielawinfo-checkbox-others | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other. |
| cookielawinfo-checkbox-performance | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance". |
| viewed_cookie_policy | 11 months | The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data. |
